
Healthcare IT support in Eastern Massachusetts, Rhode Island and the Charlotte, NC area
IT support for healthcare practices, built around patients and HIPAA
When the EHR is slow, patients wait. When a phishing email gets through, patient data is at risk. We keep your practice’s systems running, protect patient information, sign your business associate agreement and help you meet HIPAA, so your team can focus on care.
Prefer the phone? Call 774-222-5500.
- Soteria Award winner: Most Trusted MSP in North America
- Microsoft Partner
- Certified Trust Level 2 IT provider
The short version
Fairoaks IT is an independent, owner-led managed IT and cybersecurity company serving medical, dental, behavioral health, physical therapy and orthotics practices, and yes, even animal and veterinary healthcare, across Eastern Massachusetts, Rhode Island and the Charlotte, NC area from offices in Franklin, MA and Belmont, NC. We support the systems practices run on, including athenahealth, eClinicalWorks, NextGen, Dentrix, Eaglesoft, Open Dental, SimplePractice and TherapyNotes. We sign business associate agreements and help practices meet HIPAA with security risk analyses, written policies, staff training, penetration testing and vulnerability scanning, and our own organization undergoes independent audits. Fairoaks IT won the Soteria Award for Most Trusted MSP in North America, and CEO Adam Crossley leads our healthcare work.
Sound familiar?
A normal week at a lot of practices we talk to.
The EHR freezes with a full waiting room.
Check-in stops, charting stops, and patients start checking their watches.
A “patient” emails an attachment.
It looks like a referral or a lab result. It’s one of the most common ways into a practice.
Nobody can find your HIPAA risk analysis.
It was done years ago, if it was done at all, and it’s the first thing an auditor asks for.
Your office manager is also your IT person.
Every hour spent fixing printers is an hour not spent on patients and billing.
The imaging computer runs software nobody updates.
It works, so nobody touches it, and it sits on the same network as everything else.
Your IT company has never offered a BAA.
If they can reach patient data, HIPAA says they need one.
None of these are really computer problems. They’re patient care problems, compliance problems and time problems. And if you’re paying an IT company and still managing all of it yourself, something’s wrong. You should be running the practice, not managing your IT company.
What we take responsibility for, from the front desk to the exam room
EHR and practice software
athenahealth, eClinicalWorks, NextGen, Dentrix, Eaglesoft, Open Dental, SimplePractice, TherapyNotes and more, running fast, with vendor issues handled for you.
HIPAA compliance support
Security risk analyses, written policies, staff training, penetration testing and vulnerability scanning, and a signed business associate agreement.
Cybersecurity
Security updates, endpoint protection and 24/7 monitoring come standard. Most of our plans add staff training and phishing simulations, and our advanced security option adds a 24/7 security operations center.
Imaging, devices and the front desk
Imaging workstations, card readers, check-in and label printers, scanners and phones kept working, with medical devices on their own network segment.
Backup and recovery
Patient records and practice data backed up where ransomware can’t reach them, and test-restored, so a bad day doesn’t close your doors.
Secure communication
Encrypted email, secure file sharing and Microsoft 365 set up for patient privacy, with multi-factor authentication on every login.
Part of a larger group, or have an in-house IT person? Co-managed IT gives them a full team behind them instead of replacing them. How co-managed IT works
Where the HIPAA Security Rule update stands
As of October 2026
- The current Security Rule is what’s enforced.HHS’s Office for Civil Rights enforces the existing HIPAA Security Rule today, including the requirement for an accurate and thorough risk analysis.
- A major update is still proposed.In December 2024, HHS proposed the biggest Security Rule overhaul in a decade. It would make protections like multi-factor authentication and encryption mandatory, and add requirements like an asset inventory, vulnerability scanning and penetration testing.
- Final action has slipped.As of fall 2026, the update hadn’t been finalized, and HHS’s regulatory agenda now targets July 2027 for final action. Practices would get a compliance window after that.
- Breach rules haven’t changed.A breach of unsecured patient information still triggers notice to patients within 60 days, and to HHS, with media notice when 500 or more residents of a state are affected.
Bottom line: the protections in the proposal are good practice now. We help practices put them in place before they’re required, and we update this section as HHS acts.
HIPAA, done right
HIPAA expects every practice to protect patient information with real safeguards, documented and kept current. Here’s how we help:
- We sign business associate agreements with our healthcare clients
- Security risk analysis, the foundation HIPAA requires
- Written HIPAA security policies, with an easy way for staff to acknowledge them
- Staff security training and phishing simulations
- Penetration testing and vulnerability scanning
- Encryption and multi-factor authentication on every system with patient data
- A breach response plan, including HHS notification timelines
- Our own organization undergoes independent audits, so we hold ourselves to the standard we help you meet
Will you sign our BAA?
Yes. Any IT provider that can access systems holding patient information is a business associate under HIPAA. We sign business associate agreements with our healthcare clients before work begins.
Healthcare software we support
We keep these running, along with the servers, networks, imaging workstations and integrations behind them. (Yes, even animal and veterinary healthcare.)
In our clients’ own words
“Fairoaks IT has always been there for us when we’ve needed them. If a problem can’t be solved remotely, they head right over in person to get it fixed. We love how responsive they are and the knowledge of their staff. Everyone there truly cares about our business and what’s right for us.”
 Taylor MacElhineyBilling Coordinator, Boston Orthotics
“Each person from Fairoaks IT has been pleasant, professional, and clear on each step that’s been taken… We commend you for creating such an environment in your IT business.”
“It is a mean world out there in all respects, and Fairoaks IT have diligently kept us informed and trained to avoid click bait and phishing emails.”
 Rob EnglishOwner, Chemical Solutions
How working with us starts
-
Discovery call
A straightforward conversation about your practice, your software and what isn’t working. No pitch and no pressure. If we’re not the right fit, we’ll tell you.
-
Assessment
We review your network, EHR setup, imaging and front-desk devices, Microsoft 365, backups, security, and where your HIPAA risk analysis and policies stand. You get a plain-English report. No scare tactics, just facts.
-
Plan and proposal
A plan built around your practice and budget, with monthly support and one-time projects clearly separated and every cost explained up front.
-
Onboarding, then ownership
A signed business associate agreement, then onboarding scheduled around patient hours, with a named point of contact and weekly check-ins until it’s done. From there, we take responsibility.
What you can count on
Help in minutes, not hours
Our average time to start on a support issue is under 12 minutes, with live support during business hours and after-hours support available.
No surprises
Before you sign, you’ll know exactly what’s included, what isn’t and how every cost works. It’s all in writing, and we’ll walk you through every page.
Accountable at the top
Fairoaks IT is owned and run by Tom and Adam Crossley. If something isn’t right, the people who own the company are the people who answer for it.
From our Client Bill of Rights
- Answers to your questions in plain English.
- All costs explained up front, with no hidden fees or surprise invoices.
- A single point of contact for every technology issue, including help with your other vendors.
- Your request acknowledged within an hour, appointments kept and clear communication throughout.
Healthcare IT questions, answered
Straight answers to the 30 questions practice owners, administrators and office managers ask us most.
Choosing IT support for a healthcare practice
What should a healthcare practice look for in an IT support company?
Look for a provider that already understands how a practice runs: your EHR and practice management software, imaging and front-desk devices, patient communication and HIPAA. Then check four things: will they sign a business associate agreement, how fast does a real person start on your issue, are security and backup built into the plan, and can they help with your risk analysis and policies. Ask for references from other practices, and ask how they’d onboard you without disrupting patient hours.
What does a managed IT provider do for a medical or dental practice?
A managed IT provider acts as your outsourced IT department for a predictable monthly fee. For a practice, that typically covers support for providers and staff, monitoring and maintenance of computers, servers and the network, EHR and imaging support, cybersecurity, backup, Microsoft 365 and help with HIPAA safeguards. It also covers planning, so equipment replacements and upgrades happen on your schedule instead of as emergencies.
Will you sign a business associate agreement?
Yes. Any IT provider that can access systems holding patient information is a business associate under HIPAA, and you need a signed business associate agreement before they start. Fairoaks IT signs BAAs with our healthcare clients. Be wary of any provider that hesitates, or says it doesn’t need one because it “doesn’t look at patient data.”
Can you work alongside our in-house IT person or our group’s IT team?
Yes. Co-managed IT gives your internal IT person or team a full bench behind them: help with escalations, security tools and monitoring, backup, projects, vacation coverage and after-hours help when you need it. They stay your front line and keep their day-to-day knowledge of the practice, and you stop depending on one person for everything.
Who provides healthcare IT support in Eastern Massachusetts, Rhode Island and the Charlotte, NC area?
Fairoaks IT provides managed IT, cybersecurity and HIPAA compliance support for healthcare practices throughout Eastern Massachusetts, Rhode Island and the Charlotte, NC metro area, from offices in Franklin, MA and Belmont, NC. We’ve been independent and owner-led since 1991, we won the Soteria Award for Most Trusted MSP in North America, we sign business associate agreements, and CEO Adam Crossley leads our healthcare work.
Healthcare IT in Massachusetts and Rhode Island | Healthcare IT in the Charlotte, NC area
What kinds of practices do you support?
Medical practices and specialty clinics, dental offices, behavioral health and counseling practices, physical therapy, orthotics and prosthetics, and yes, even animal and veterinary healthcare. Veterinary practices aren’t covered by HIPAA, but they hold plenty of client and payment information worth protecting, and their practice software needs the same care.
Patient care, uptime and devices
How do we keep the EHR fast and available during patient hours?
Most slowdowns come from the pieces around the EHR: aging computers, a congested network, weak Wi-Fi in exam rooms, an overdue server or an internet connection that’s too small. Keep computers on a replacement schedule, monitor the network and internet, put a backup internet connection in place if your EHR is cloud-based, and schedule updates outside patient hours. We also work directly with your EHR vendor when the problem is on their side.
What happens if our systems go down or we’re hit with ransomware?
With the right preparation, a bad day instead of a closed practice. That takes backups stored where ransomware can’t reach them and tested regularly, a recovery plan that says how fast your EHR and practice data come back, written downtime procedures so the front desk and clinicians can keep seeing patients, and support that starts fast. Fairoaks IT’s average time to start on a support issue is under 12 minutes.
Should our EHR be cloud-based or on a server in the office?
It depends on your software and your practice. Cloud systems like athenahealth take servers off your plate but depend on a reliable internet connection. Many dental and specialty systems, like Dentrix, Eaglesoft and Open Dental, often run on an office server, which needs proper backup, security and replacement planning. Some vendors offer hosted versions too. We lay out the options, costs and security trade-offs side by side.
How should imaging equipment and medical devices be handled on the network?
Carefully, and on their own network segment. Imaging systems and other devices often run older software that can’t be updated as easily as office computers, so separating them limits what an attacker or a virus can reach. Vendor remote access should be controlled and turned on only when it’s needed. We document every connected device and coordinate with your device vendors when something needs their expertise.
How do we support providers working from home or across several locations?
With company-managed devices, secure remote access and multi-factor authentication on every login, so patient information never lives on personal computers. Multi-location practices get the same standards everywhere: the same network design, security tools and support team, with each location connected securely to your EHR and phones.
What happens when someone needs help outside business hours?
Fairoaks IT provides live support during business hours, with after-hours support available for emergencies, and our average time to start on a support issue is under 12 minutes. For practices with early, late or weekend hours, we plan ahead: monitoring that flags problems overnight, clear instructions for staff, and an agreed process for urgent issues.
HIPAA and compliance
What does HIPAA require from a practice’s IT?
The HIPAA Security Rule requires administrative, physical and technical safeguards for electronic patient information. In practice that means a risk analysis, security policies, workforce training, access controls so people only see what they need, audit controls, protection against tampering, secure transmission, contingency planning with backups, and business associate agreements with vendors who handle patient data. It all needs to be documented and kept current.
What is a HIPAA security risk analysis, and how often do we need one?
A security risk analysis identifies where patient information lives in your practice, the threats and weaknesses that could expose it, and how you’re addressing each one. HIPAA requires it, and it’s the first document regulators ask for after a breach. The current rule doesn’t set a fixed schedule, but it should be reviewed regularly and whenever your systems change; most practices review it yearly. We perform risk analyses and help you act on what they find.
Is the HIPAA Security Rule changing?
A major update has been proposed but not finalized. In December 2024, HHS proposed making protections like multi-factor authentication and encryption mandatory, and adding requirements like an asset inventory, vulnerability scanning and penetration testing. As of fall 2026 it hadn’t been finalized, and HHS now targets July 2027 for final action. The current rule is what’s enforced today, but the proposed protections are good practice now.
What do we have to do after a breach of patient information?
Act fast and follow your written plan. Under the HIPAA Breach Notification Rule, affected patients must be notified without unreasonable delay and no later than 60 days after discovery. Breaches affecting 500 or more people must also be reported to HHS within 60 days, along with notice to prominent media when 500 or more residents of a state are affected; smaller breaches are reported to HHS annually. State breach laws can add their own requirements.
Can we email or text patients?
Yes, with the right safeguards. HIPAA allows it, but messages containing patient information should be encrypted, and patients should be told about the risks if they ask for unencrypted messages. Use a patient portal or secure messaging for anything sensitive, require multi-factor authentication on staff email, and write down the rules so everyone follows them the same way. Our guide includes a patient email and texting policy starter.
Does HIPAA apply to veterinary practices?
No. HIPAA protects human health information, so animal records aren’t covered. But veterinary practices still hold client names, addresses and payment information, and state data security and breach laws can apply to it. The same protections, like multi-factor authentication, backups and staff training, make sense either way.
Do you provide HIPAA policies and staff training?
Yes. We help practices create the written HIPAA security policies they need and set up an easy way for every employee to acknowledge them. Staff security training and phishing simulations are part of most of our plans, so your team learns to spot the emails that cause most breaches.
Security and fraud
Why are healthcare practices targeted by cybercriminals?
Because patient records are valuable, and practices can’t afford downtime. A practice that can’t see patients is under enormous pressure to pay a ransom, and health records can be sold or used for identity and insurance fraud. The 2024 Change Healthcare attack also showed how one breach at a vendor can disrupt practices nationwide. The defense is layered: multi-factor authentication, endpoint protection, email filtering, tested backups and trained staff.
What security controls should every practice have?
Multi-factor authentication on email, the EHR and remote access; encryption on laptops and in transit; endpoint protection on every computer and server; email filtering; security updates on a schedule; backups stored where ransomware can’t reach them and test-restored; staff training with phishing simulations; medical devices on their own network segment; and regular reviews of who has access to what.
How should we handle access when staff leave or change roles?
Remove access the day someone leaves, from every system: the EHR, email, practice management, patient portal, remote access and shared accounts. When people change roles, adjust their access to match. Shared logins at the front desk make it impossible to know who did what, so give each person their own. Our guide includes a staff onboarding and offboarding checklist.
Can our staff use AI tools with patient information?
Only tools approved for patient data, which generally means a business-grade tool covered by a business associate agreement. Free and personal AI accounts may keep what your team types in, so patient names, records and images should never go into them. A short AI use policy should name the approved tools, list what never goes in and say who to ask first.
What security controls do cyber insurance carriers usually require?
Most carriers ask about the same core controls: multi-factor authentication on email and remote access, endpoint detection and response, backups that are offline or can’t be altered and are tested, security awareness training and timely patching. Many overlap with HIPAA’s safeguards, so one well-run program can satisfy both. Make sure every yes on the application is true. Your insurance agent has the final word on your policy.
Cost, contracts and switching providers
How much does IT support cost for a healthcare practice?
It depends on how many people and devices you support, how many locations you have, your imaging and device needs, your compliance requirements and how much is included in the monthly fee versus billed separately. Most providers price per user or per device each month, with onboarding and projects quoted separately. Compare what’s included, not just the total. Our IT Buyer’s Guide explains the pricing models and the contract terms to watch for.
What’s included in a managed IT plan, and what costs extra?
A good plan lists both clearly. Monthly plans typically include support for your users, monitoring and maintenance, security tools, backup and Microsoft 365 management. Hardware, software licenses, EHR subscriptions and larger projects, like a server replacement, a new location or a risk analysis, are usually quoted separately. Ask every provider for their exclusions in writing. At Fairoaks IT, we explain all costs up front, so there are no hidden fees or surprise invoices.
How long are managed IT contracts, and what if it isn’t working?
Many managed IT agreements run for multiple years, which locks in your rate and gives your provider reason to invest in your environment. What matters is what happens if things aren’t working, so ask every provider two questions: what happens if you don’t deliver, and how are price increases handled? Get both answers in writing. At Fairoaks IT, ours are spelled out in our agreement, and we’ll walk you through every page before you sign.
How do we switch IT providers without disrupting patient care?
With a plan built around your schedule. A good transition starts with a signed business associate agreement, then documents every system, password, license and vendor, including your EHR, imaging and phones, before a coordinated handoff from your current provider. Changes happen outside patient hours. Urgent risks like backups and multi-factor authentication get fixed first. Fairoaks IT assigns a point of contact and holds weekly check-ins until onboarding is complete.
What happens during a free IT assessment?
We review your network, servers, computers, EHR setup, imaging and front-desk devices, Microsoft 365, backups and security with our proprietary 27-point assessment, and look at where your HIPAA risk analysis and policies stand. You get a plain-English summary of what’s working, what’s at risk and what to fix first. No scare tactics, just facts. It starts with a discovery call.
Is our practice big enough for managed IT?
If you have around 10 or more people on computers every day, or patient care stops when technology does, managed IT usually makes sense. Smaller practices carry the same HIPAA obligations as large ones, and a single breach or outage can hurt a small practice more. A short discovery call is the fastest way to know.
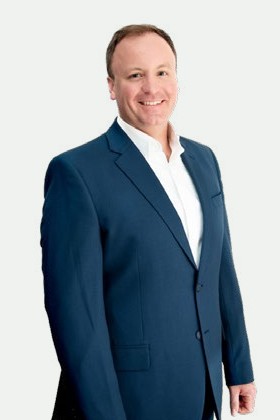
CEO
The person behind our healthcare work
Adam Crossley is CEO of Fairoaks IT and leads our healthcare work. Before IT, he worked at Sikorsky on the Navy Seahawk program and as an internal consultant and manager for United Technologies across the US, Europe and Asia.
Adam holds a degree in Operations Management from UMass Dartmouth, a Master of Science in Global Supply Chain from Indiana University and an MBA from UMass Amherst. He co-owns Fairoaks IT with his father, Tom Crossley, who founded the company in 1991. Adam’s books include The Compliance Formula: Successful Strategies of CMMC Compliant Companies, Cyberattack: How to Defend Your Business and Protect Your Bottom Line, and Cybersecurity: The Silent Battlefield, and he has been featured in MSP Success Magazine.
Local healthcare IT support from two offices
Eastern Massachusetts and Rhode Island
Served from our office at 1000 Franklin Village Dr, Suite 303, Franklin, MA 02038. Practices across Greater Boston, MetroWest, Worcester County, the South Shore and Rhode Island.
Charlotte, NC metro
Served from our office at 32 North Main Street, Suite 206, Belmont, NC 28012. Practices across Charlotte, Gastonia, Concord, Huntersville, Monroe, Rock Hill and Fort Mill.
Contact us today to schedule your discovery call
What happens next:
- We’ll reach out to set up a time that works around your patient schedule.
- A short conversation about your practice and what isn’t working.
- If it makes sense for both of us, we’ll plan an assessment.
Prefer the phone? Call 774-222-5500.
Schedule your discovery call
Book a time at fairoaksit.com/discoverycall or call 774-222-5500.