
Managed security services in Eastern Massachusetts, Rhode Island and the Charlotte, NC area
Managed security services that watch your business around the clock
Attackers don’t keep business hours, and neither does our security operations center. We layer endpoint, network, cloud and AI detection and response with training, testing and compliance help, for businesses we fully manage and for companies with their own IT teams.
Prefer the phone? Call 774-222-5500.
- Soteria Award winner: Most Trusted MSP in North America
- Microsoft Partner
- Certified Trust Level 2 IT provider
The short version
Fairoaks IT provides managed security services for small and midsize businesses across Eastern Massachusetts, Rhode Island and the Charlotte, NC area from offices in Franklin, MA and Belmont, NC. Our advanced security option adds a 24/7 security operations center with advanced endpoint detection and response, network detection and response, threat detection and response for Microsoft 365 and Google Workspace, AI detection and response, vulnerability scanning, log retention and DNS protection. We also provide staff training and phishing simulations, penetration testing, incident response with forensic investigation available, virtual CISO services, and help with HIPAA, CMMC and NIST 800-171, the FTC Safeguards Rule, IRS Publication 4557 and PCI DSS. Businesses with their own IT teams can add our security services as co-managed security. CEO Adam Crossley, author of Cyberattack and Cybersecurity: The Silent Battlefield, leads our security work.
Sound familiar?
What we hear most from businesses before they call us about security.
Antivirus is the whole security plan.
It catches yesterday’s threats. Today’s attackers log in with stolen passwords.
An alert fires at 2 a.m., and nobody sees it.
By morning, the attacker has had six hours inside your network.
A customer or insurer asks for proof.
Multi-factor authentication, testing, training and logs, and the answers are due Friday.
Employees use AI tools nobody approved.
And attackers use AI to write better phishing emails than ever.
Your IT person is stretched too thin to watch for threats.
Keeping things running leaves no time for hunting attackers.
Nobody has tested whether an attacker could get in.
You’ll find out eventually. Better to find out from a penetration test.
None of these are really technology problems. They’re visibility problems. You can’t stop what nobody is watching, and you can’t prove protection you can’t show.
What our managed security services include
24/7 security operations center
Security analysts watching for threats around the clock and responding when something suspicious happens, through our advanced security option.
Endpoint, network and cloud detection and response
Advanced endpoint detection and response, network detection and response, and threat detection and response for Microsoft 365 and Google Workspace.
AI detection and response
AIDR identifies malicious uses of AI that target or operate inside your environment, and responds when it finds them.
Vulnerability scanning and penetration testing
Regular scans for weaknesses and penetration tests that show whether an attacker could actually get in.
Training and phishing simulations
Security awareness training and simulated phishing emails, so your team learns to spot the attacks that cause most breaches.
Incident response and virtual CISO
Incident response with forensic investigation available, plus a virtual CISO to lead your security program and planning.
Already have IT staff? Our co-managed security adds the SOC, tools and expertise without replacing your team. How co-managed security works
Security in layers
No single tool stops every attack. These layers work together, and our team watches them around the clock:
- A 24/7 security operations center that investigates alerts and responds
- Advanced endpoint detection and response on every computer and server
- Network detection and response that spots suspicious traffic inside your network
- Threat detection and response for Microsoft 365 and Google Workspace
- AI detection and response (AIDR) that identifies malicious uses of AI
- Vulnerability scanning and penetration testing
- Log retention for investigations and compliance
- DNS protection that blocks malicious websites before they load
- Staff training and phishing simulations
- Incident response, with forensic investigation available
- Virtual CISO services to lead your security program
Security for companies with their own IT
Many businesses already have an IT person or team. Co-managed security adds our security operations center, detection and response tools, testing and expertise alongside them, without taking over the work they already do.
Compliance requirements we help with
We help businesses meet the technical side of these requirements, from risk assessments and policies to testing and the documentation auditors ask for.
In our clients’ own words
“It is a mean world out there in all respects, and Fairoaks IT have diligently kept us informed and trained to avoid click bait and phishing emails… If you are shopping for a new IT support partner, then focus on results and not on price. What is the cost of your business being down versus trying to save a few pennies on monthly or hourly fees?”
 Rob EnglishOwner, Chemical Solutions
“From white glove service to flexible plans that allow us to leverage their team, you can pick which one… Fairoaks IT has delivered EVERY TIME.”
 Chris KnocheVice President, IT and Cybersecurity Operations, Sontiq
“Not needing to worry about the security of our network and customer data is a huge benefit. Knowing that Fairoaks IT is keeping us secure allows us to focus on our business.”
 Mark TravisPresident, Mass Installation
How working with us starts
-
Discovery call
A straightforward conversation about your business and what isn’t working. No pitch and no pressure. If we’re not the right fit, we’ll tell you.
-
Assessment
We review your security tools, Microsoft 365 or Google Workspace setup, backups, remote access, staff training and any customer, insurance or compliance requirements. You get a plain-English report. No scare tactics, just facts.
-
Plan and proposal
A recommendation built around your business and budget, with monthly support and one-time projects clearly separated and every cost explained up front.
-
Onboarding, then ownership
A named point of contact and weekly check-ins until onboarding is done, scheduled around your busy times. From there, we take responsibility.
What you can count on
Help in minutes, not hours
Our average time to start on a support issue is under 12 minutes, with live support during business hours and after-hours support available.
No surprises
Before you sign, you’ll know exactly what’s included, what isn’t and how every cost works. It’s all in writing, and we’ll walk you through every page.
Accountable at the top
Fairoaks IT is owned and run by Tom and Adam Crossley. If something isn’t right, the people who own the company are the people who answer for it.
From our Client Bill of Rights
- Answers to your questions in plain English.
- All costs explained up front, with no hidden fees or surprise invoices.
- A single point of contact for every technology issue, including help with your other vendors.
- Your request acknowledged within an hour, appointments kept and clear communication throughout.
Managed security questions, answered
Straight answers to the 20 questions business owners, managers and IT leaders ask us most.
Managed security basics
What are managed security services?
Managed security services means an outside team protects your business around the clock: watching for threats, investigating alerts, responding to attacks, testing your defenses, training your staff and helping you meet compliance requirements. It gives a small or midsize business the kind of security program large companies build in-house, without hiring a security department.
What is a security operations center, and do we need one?
A security operations center, or SOC, is a team of security analysts that watches for threats around the clock and responds when something suspicious happens, like a login from an unusual country at 2 a.m. or ransomware starting to spread. Basic monitoring catches failing hardware and missed updates; a SOC catches attackers. Our advanced security option includes a 24/7 SOC.
How is endpoint detection and response different from antivirus?
Antivirus looks for known bad files. Endpoint detection and response, or EDR, watches what happens on each computer and server, like unusual processes, credential theft or encryption starting, and can isolate a device to stop an attack in progress. Paired with a SOC, someone investigates and acts on what it finds. Most cyber insurance carriers now expect it.
What is AI detection and response?
AI detection and response, or AIDR, identifies malicious uses of AI that target or operate inside your environment, and responds when it finds them. As attackers use AI to write convincing phishing emails, automate attacks and impersonate people, it adds another layer alongside endpoint, network and cloud detection and response.
Do you offer security for companies that have their own IT team?
Yes. Co-managed security adds our security operations center, detection and response tools, testing and expertise alongside your internal IT person or team, without taking over the work they already do. It’s a common fit for businesses whose IT staff are busy keeping things running and don’t have time to watch for threats around the clock.
Threats and protection
What are the biggest cyber threats to small and midsize businesses?
Phishing and stolen passwords, business email compromise and ransomware cause most of the damage. The FBI’s 2025 Internet Crime Report recorded about $3 billion in business email compromise losses alone. The defense is layered: multi-factor authentication, email filtering, endpoint detection and response, tested backups, a team watching around the clock and staff who know what a bad email looks like.
How do you protect Microsoft 365 and Google Workspace?
Start with multi-factor authentication for everyone, separate admin accounts, sensible sharing settings and email filtering. Our advanced security option adds threat detection and response for Microsoft 365 and Google Workspace, which watches for suspicious sign-ins, inbox rules that forward mail to attackers and other signs of a compromised account, with the SOC responding when something is wrong.
What happens when the SOC spots a threat?
Analysts investigate to confirm it’s real, then act: isolating an infected computer, disabling a compromised account or blocking malicious traffic to stop the attack from spreading. We notify you, fix what was affected and look at how it happened so it doesn’t happen again. If it’s a serious incident, incident response takes over, with forensic investigation available.
How do we protect the business from AI-powered scams?
Attackers now use AI to write flawless phishing emails and even imitate voices. Process beats technology here: verify any unusual request for money, gift cards or passwords by calling a number you already have, no matter how convincing the message is. Training and phishing simulations keep that habit sharp, and AI detection and response adds a technical layer.
How often should we test our security?
Vulnerability scanning should run regularly, so new weaknesses are found and fixed quickly. Penetration testing, where testers try to break in the way an attacker would, is commonly done at least once a year and after major changes. Some rules and customers require specific schedules, like the FTC Safeguards Rule for tax and financial firms. We provide both.
Compliance, insurance and incidents
Which compliance requirements do you help with?
We help businesses meet the technical side of HIPAA for healthcare, CMMC and NIST 800-171 for defense suppliers, the FTC Safeguards Rule and IRS Publication 4557 for tax and accounting firms, and PCI DSS for businesses that take card payments. That includes risk assessments, written security policies, security controls, testing and the documentation auditors and customers ask for.
What security controls do cyber insurance carriers require?
Most carriers ask about the same core controls: multi-factor authentication on email and remote access, endpoint detection and response, backups that are offline or can’t be altered and are tested, security awareness training and timely patching. Some ask about monitoring and incident response plans. Make sure every yes on the application is true. Your insurance agent has the final word on your policy.
What is a virtual CISO?
A virtual chief information security officer is an experienced security leader you share instead of hire. They assess your risks, set priorities, write and maintain security policies, prepare you for audits and customer questionnaires, and report progress to leadership. It’s a practical way for a smaller business to get security leadership without a full-time executive salary.
Why does log retention matter?
Logs record who signed in, what changed and what happened on your systems. When something goes wrong, they’re how investigators figure out what an attacker did and what data was involved. Many compliance requirements and customer contracts also expect logs to be kept for a set period. Our advanced security option includes log retention.
What happens during a security incident?
Act fast and follow the plan. Contain the threat, preserve evidence, call your cyber insurance carrier before hiring outside help, and work out what was affected. We handle incident response, with forensic investigation available when you need to know exactly what happened. How incident response is handled is spelled out in your agreement before you sign.
Cost and getting started
What do managed security services cost?
It depends on how many people, devices and cloud accounts you protect, which layers you need, whether you need testing or a virtual CISO, and your compliance requirements. Most providers price per user or per device each month, with testing and projects quoted separately. Compare what’s included and who is actually watching, not just the price. Our IT Buyer’s Guide explains typical pricing and contract terms.
Is security included in managed IT?
Yes, at different levels. Security updates, endpoint protection and 24/7 monitoring come standard with every Fairoaks IT plan. Most of our plans add staff training and phishing simulations, and our advanced security option adds the 24/7 security operations center, detection and response layers and log retention. We recommend the level that fits your risk, insurance and compliance needs.
How long are managed IT contracts, and what if it isn’t working?
Many managed IT agreements run for multiple years, which locks in your rate and gives your provider reason to invest in your environment. What matters is what happens if things aren’t working, so ask every provider two questions: what happens if you don’t deliver, and how are price increases handled? Get both answers in writing. At Fairoaks IT, ours are spelled out in our agreement, and we’ll walk you through every page before you sign.
What happens in a security assessment?
We review your security tools, Microsoft 365 or Google Workspace setup, backups, remote access, staff training and any customer, insurance or compliance requirements with our proprietary 27-point assessment. You get a plain-English summary of what’s protected, what’s exposed and what to fix first. No scare tactics, just facts. It starts with a discovery call.
Who provides managed security services in Eastern Massachusetts, Rhode Island and the Charlotte, NC area?
Fairoaks IT provides managed security services for businesses throughout Eastern Massachusetts, Rhode Island and the Charlotte, NC metro area, from offices in Franklin, MA and Belmont, NC. We’ve been independent and owner-led since 1991, we won the Soteria Award for Most Trusted MSP in North America, and our average time to start on a support issue is under 12 minutes.
Managed IT in Massachusetts and Rhode Island | Managed IT in the Charlotte, NC area
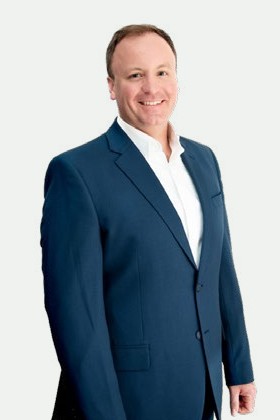
CEO
The person behind our security work
Adam Crossley is CEO of Fairoaks IT and leads our cybersecurity and compliance work. Before IT, he worked at Sikorsky on the Navy Seahawk program and as an internal consultant and manager for United Technologies across the US, Europe and Asia.
Adam’s books include Cyberattack: How to Defend Your Business and Protect Your Bottom Line, Cybersecurity: The Silent Battlefield and The Compliance Formula: Successful Strategies of CMMC Compliant Companies, and he has been featured in MSP Success Magazine. He holds a degree in Operations Management from UMass Dartmouth, a Master of Science in Global Supply Chain from Indiana University and an MBA from UMass Amherst, and co-owns Fairoaks IT with his father, Tom Crossley, who founded the company in 1991.
Local managed security from two offices
Eastern Massachusetts and Rhode Island
Served from our office at 1000 Franklin Village Dr, Suite 303, Franklin, MA 02038. Businesses across Greater Boston, MetroWest, Worcester County, the South Shore and Rhode Island.
Charlotte, NC metro
Served from our office at 32 North Main Street, Suite 206, Belmont, NC 28012. Businesses across Charlotte, Gastonia, Concord, Huntersville, Monroe, Rock Hill and Fort Mill.
Contact us today to schedule your discovery call
What happens next:
- We’ll reach out to set up a time that works around your schedule.
- A short conversation about your business and what isn’t working.
- If it makes sense for both of us, we’ll plan an assessment.
Prefer the phone? Call 774-222-5500.
Schedule your discovery call
Book a time at fairoaksit.com/discoverycall or call 774-222-5500.