
CMMC and NIST 800-171 readiness for defense suppliers in Eastern Massachusetts, Rhode Island and the Charlotte, NC area
Get ready for CMMC and NIST 800-171, explained in plain English
If you make parts, products or drawings for the defense supply chain, your customers expect you to protect their data, and the rules keep changing. We find where your controlled data lives, close the gaps, build the documentation and keep you ready, so you can keep bidding with confidence.
Prefer the phone? Call 774-222-5500.
- Soteria Award winner: Most Trusted MSP in North America
- Microsoft Partner
- Certified Trust Level 2 IT provider
Where CMMC stands
As of October 2026
- Phase 1 is in effect.Since November 10, 2025, applicable defense contracts can require CMMC Level 1 or Level 2 self-assessments, with scores posted in SPRS and affirmed every year.
- Phase 2 is paused.Third-party (C3PAO) certification was set to become a condition of award on November 10, 2026. The Defense Department suspended that step on July 13, 2026 while it reviews the program. During the pause, new contracts can require only Level 1 or Level 2 self-assessments.
- A review is underway.The CMMC Reform Task Force’s review closed in September 2026. Its recommendations hadn’t been made public as of early October, and no new date for Phase 2 has been set.
- The underlying rules haven’t changed.DFARS 252.204-7012 still requires NIST SP 800-171 protections for controlled unclassified information and reporting of cyber incidents within 72 hours, and primes still flow requirements down to their suppliers.
- Self-attestation carries real risk.The Justice Department continues to pursue false cybersecurity claims under the False Claims Act. In September 2026, a major aerospace supplier agreed to a $2 million settlement over alleged NIST SP 800-171 failures.
Bottom line: the deadline for third-party certification moved, but the security requirements didn’t. We update this section as the Defense Department announces decisions.
The short version
Fairoaks IT helps defense suppliers get ready for CMMC and NIST SP 800-171 and stay ready. We find where federal contract information and controlled unclassified information live, run a gap assessment against the 110 NIST SP 800-171 requirements, build the system security plan and plan of action, support your SPRS score, close the gaps, set up separate environments like Microsoft 365 GCC High or an isolated enclave when they make sense, and support you through assessments. We’ve helped numerous manufacturers, large and small, that supply defense primes. Fairoaks IT is independent and owner-led since 1991, won the Soteria Award for Most Trusted MSP in North America, and is led by CEO Adam Crossley, who worked at Sikorsky on the Navy Seahawk program before entering IT. We serve Eastern Massachusetts, Rhode Island and the Charlotte, NC area from offices in Franklin, MA and Belmont, NC.
Does CMMC apply to you?
Federal contract information (FCI)
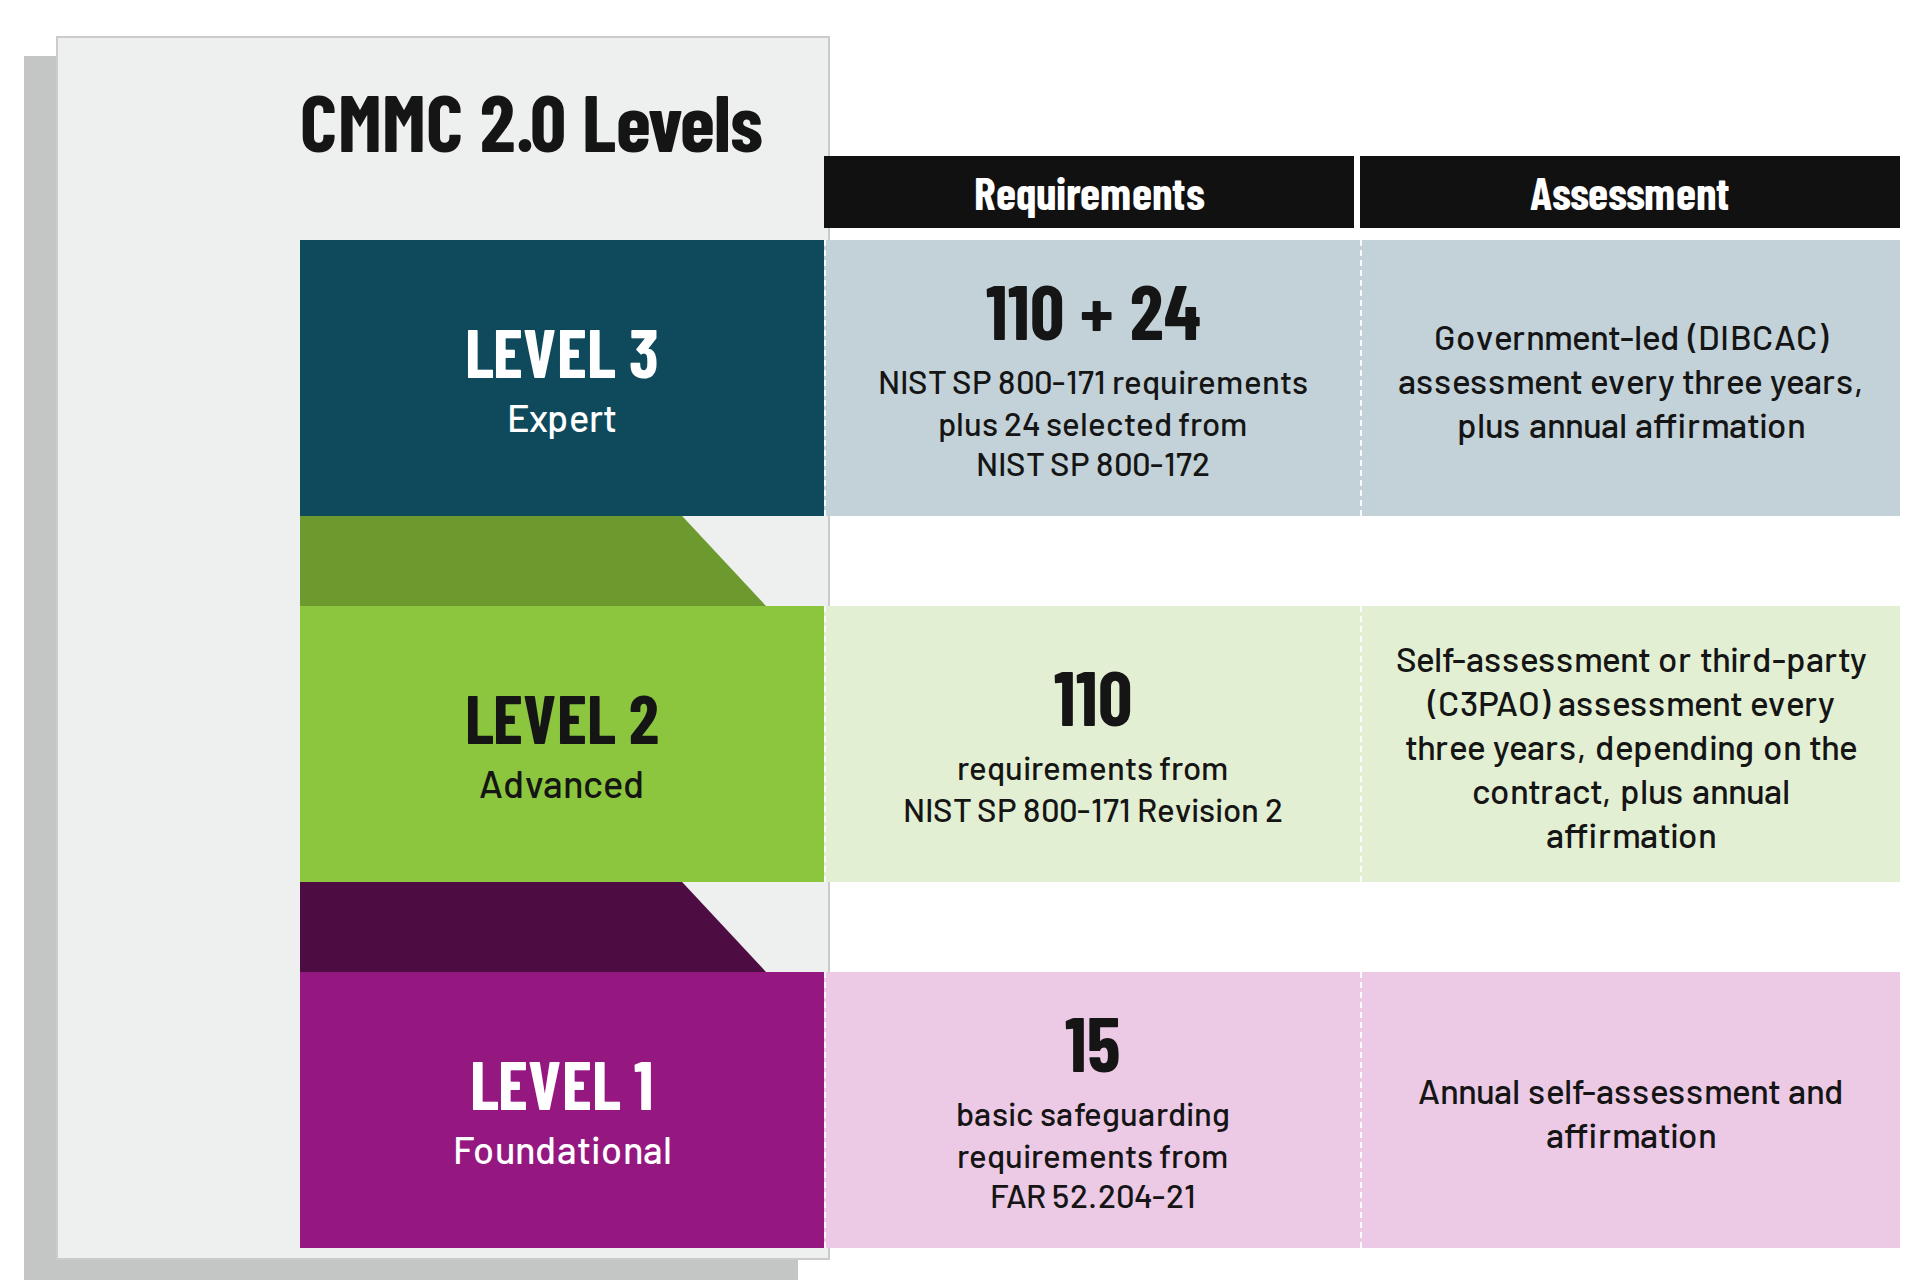
Information the government provides or generates under a contract that isn’t meant for public release, like contract details, quantities and delivery schedules. If you handle only FCI, Level 1 applies.
Controlled unclassified information (CUI)
More sensitive information that has to be safeguarded, such as certain technical drawings, specifications and export-controlled data. If you handle CUI, Level 2 applies, and a small number of the most sensitive programs require Level 3.
Many suppliers fall under CMMC through a prime contractor or a higher-tier subcontractor without realizing it. Check your contracts and purchase orders for DFARS 252.204-7012, 252.204-7019, 252.204-7020 or 252.204-7021, and ask your customer what level they expect.
How we get you ready and keep you ready
Find where controlled data lives
Map which systems, folders, people and suppliers touch FCI and CUI, so you protect the right things and keep your scope as small as possible.
Gap assessment
Measure your environment against the 110 NIST SP 800-171 requirements and show what’s met, partly met or missing, in plain English.
System security plan
Document your environment and how each requirement is met. The system security plan is the first document primes and assessors ask for.
Plan of action and milestones
A prioritized, dated plan for every gap, so you can show progress, not just problems.
SPRS score support
Calculate your NIST SP 800-171 self-assessment score accurately and support you in posting and affirming it in SPRS.
Remediation
Close the gaps: multi-factor authentication, encryption, logging, access control, secure configuration, and production equipment on its own network segment.
Separate environments for controlled data
Microsoft 365 GCC High or an isolated enclave when it makes sense, so CUI stays in a smaller space that’s easier to protect and assess.
Policies and procedures
Policy and procedure templates that match the requirements, with guidance on making them fit how your company actually works.
Ongoing monitoring and assessment support
Security monitoring and periodic reviews to keep you ready, plus help answering assessor and prime requests when it’s time to be assessed.
Readiness work is scoped as a project or compliance add-on. It fits alongside our managed IT plans, your internal IT team or your current IT provider.
Fairoaks IT doesn’t issue CMMC certifications. Level 2 certification assessments are performed by accredited third-party assessment organizations (C3PAOs), and Level 3 assessments by the government. Our job is to get you ready for those assessments, or for your own self-assessment, and keep you ready afterward. Keeping the people who prepare you separate from the people who assess you protects you.
In our clients’ own words
“We get the support of a whole team of professionals that have the specialties we need, for example network specialists, server experts, etc… Fairoaks IT truly knows all of us by name and what we do. They even became very familiar with our manufacturing processes and machines in order to truly understand our environment.”
 Dave DevinePierce Aluminum Company
“Fairoaks IT has provided KPM the feel of a friendly internal IT resource that everyone knows but with the breadth of knowledge that comes from having multiple technicians with decades of experience… As we grow, Fairoaks IT adapts.”
 Winston AndersonGlobal Information Systems Manager, KPM Analytics
“Tom and Adam are always accessible too, so when we do need to review our account and service, you are available to us.”
 Kevin LagasseExecutive Vice President, The Lagasse Group
How working with us starts
-
A conversation
We talk through your contracts, the data you handle, what your customers are asking for and your timeline. No pitch and no pressure.
-
Readiness assessment
We scope where FCI and CUI live and measure your environment against NIST SP 800-171. You get a plain-English picture of where you stand. No scare tactics, just facts.
-
Roadmap
Your system security plan, plan of action, current SPRS score and a realistic budget and timeline, with every cost explained up front.
-
Remediation, then staying ready
We close the gaps, set up separate environments where they make sense, and keep you ready with monitoring, annual affirmation support and help on assessment day.
What you can count on
Help in minutes, not hours
Our average time to start on a support issue is under 12 minutes, with live support during business hours and after-hours support available.
No surprises
Before you sign, you’ll know exactly what’s included, what isn’t and how every cost works. It’s all in writing, and we’ll walk you through every page.
Accountable at the top
Fairoaks IT is owned and run by Tom and Adam Crossley. If something isn’t right, the people who own the company are the people who answer for it.
From our Client Bill of Rights
- Answers to your questions in plain English.
- All costs explained up front, with no hidden fees or surprise invoices.
- A single point of contact for every technology issue, including help with your other vendors.
- Your request acknowledged within an hour, appointments kept and clear communication throughout.
CMMC and NIST 800-171 questions, answered
Straight answers to the 24 questions defense suppliers ask us most, current as of October 2026.
CMMC basics
What is CMMC?
CMMC, the Cybersecurity Maturity Model Certification, is the Defense Department’s program for verifying that contractors protect federal contract information and controlled unclassified information. It doesn’t so much create new security rules as check that the existing ones are actually in place, using three levels tied to the kind of data you handle. The program rule took effect in December 2024, and CMMC requirements began appearing in defense contracts on November 10, 2025.
How is CMMC different from NIST SP 800-171?
NIST SP 800-171 is the list of 110 security requirements for protecting controlled unclassified information. DFARS 252.204-7012 has required defense contractors handling CUI to follow it for years, largely on the honor system. CMMC is the verification layer on top: it sets how compliance is assessed and reported. If you meet NIST SP 800-171 Revision 2, you’ve met the substance of CMMC Level 2.
What are the three CMMC levels?
Level 1 covers federal contract information: 15 basic safeguarding requirements, self-assessed every year. Level 2 covers controlled unclassified information: the 110 requirements of NIST SP 800-171 Revision 2, assessed every three years either by your company or by an accredited third-party assessor, depending on the contract, with an annual affirmation. Level 3 adds 24 requirements from NIST SP 800-172 for the most sensitive programs and is assessed by the government.
What’s the difference between FCI and CUI?
Federal contract information is information the government provides or generates under a contract that isn’t meant for public release, like contract details and delivery schedules. Controlled unclassified information is more sensitive information that must be safeguarded, such as certain technical drawings, specifications and export-controlled data. FCI points to Level 1 and CUI points to Level 2. CUI should be marked by the government or your customer; if you’re not sure what you have, ask before you assume.
Do subcontractors and suppliers need CMMC?
Yes, when they handle FCI or CUI for a defense contract. DFARS 252.204-7021 requires primes to flow CMMC requirements down to subcontractors at the level that matches the information the subcontractor will handle. That means a machine shop or component supplier several tiers down can need Level 2 for the parts of the work that involve CUI.
Does CMMC apply to companies that don’t do defense work?
Not directly, because CMMC is a Defense Department program. But many commercial customers now ask suppliers about the same kinds of controls in their own security questionnaires, and cyber insurance carriers ask about many of them too. The work that prepares you for NIST SP 800-171 pays off either way.
Where things stand
Is CMMC still happening after the July 2026 pause?
Yes. The pause covers Phase 2, the step that would have made third-party certification a condition of award starting November 10, 2026. Phase 1 continues: applicable contracts can still require Level 1 or Level 2 self-assessments, and during the pause those are the only CMMC levels new contracts can require. The Defense Department’s review closed in September 2026, and as of early October its recommendations hadn’t been published and no new date had been set.
What’s still required of defense contractors right now?
Quite a bit. If your contract includes DFARS 252.204-7012, you must protect CUI under NIST SP 800-171 and report cyber incidents within 72 hours. Contracts with DFARS 252.204-7019 require a current NIST SP 800-171 assessment score in SPRS. Contracts with CMMC requirements need the specified self-assessment and an annual affirmation. And primes can still set their own requirements for suppliers.
What is SPRS, and do we need a score?
SPRS, the Supplier Performance Risk System, is where defense contractors post their NIST SP 800-171 assessment scores and CMMC status. If your contracts include DFARS 252.204-7019 or CMMC requirements, you need a current score there. Scores run from 110, with every requirement met, down into negative numbers for missing requirements, so an honest score with a plan to improve it beats an inflated one.
What’s the risk of self-attesting if we’re not really compliant?
Real. A self-assessment score and an annual affirmation are statements to the government, and the Justice Department uses the False Claims Act to pursue contractors who misrepresent their cybersecurity. In September 2026, a major aerospace supplier agreed to a $2 million settlement over alleged NIST SP 800-171 failures. The safest position is an accurate score, a documented plan to close gaps, and proof that the plan is moving.
Should we keep preparing during the pause?
Yes. The pause moved a deadline, not the security requirements. Your contracts still require NIST SP 800-171 where CUI is involved, primes are still asking, and when third-party assessments return, the companies that kept going will be ready first. Use the time to scope your controlled data, close the biggest gaps and get your documentation in order.
What’s the difference between NIST SP 800-171 Revision 2 and Revision 3?
Revision 3, published in May 2024, is the current NIST edition and reorganizes the requirements. But CMMC and defense contracts still use the 110 requirements in Revision 2, and the Defense Department hasn’t announced when that will change. Build your program to Revision 2 today, and we’ll help you map it to Revision 3 when it’s required.
Getting ready
How long does it take to get ready for CMMC?
It depends on where you start and how big your scope is. A company with modern Microsoft 365, multi-factor authentication and solid backups may need a few months to close gaps and finish its documentation. A company starting from scratch, or with controlled data spread across many systems, usually needs considerably longer. A readiness assessment gives you a realistic timeline before you commit to a date with a customer.
What are a system security plan and a plan of action?
The system security plan, or SSP, describes your environment and explains how each NIST SP 800-171 requirement is met. The plan of action and milestones, or POA&M, lists every requirement that isn’t fully met, who owns it and when it will be fixed. Both are required under NIST SP 800-171, and they’re the first documents a prime or an assessor will ask to see.
How do we find out where our controlled data lives?
Follow the data. Start with the contracts and purchase orders that involve CUI, then trace where those drawings, specs and files go: email, file shares, the ERP, engineering workstations, machine programs, removable media and the suppliers you send them to. Most companies find CUI in more places than they expected, and also find it can be pulled back into far fewer.
Can we shrink the scope of CMMC?
Usually, and it’s often the smartest move. Instead of bringing your whole company up to NIST SP 800-171, you can keep controlled data in a separate, tightly controlled environment, such as Microsoft 365 GCC High or an isolated enclave, and limit it to the people and systems that need it. A smaller scope means fewer systems to secure, document and assess. We set up these environments for clients regularly.
Do our CNC machines and production equipment fall under CMMC?
They can, if they store or process CUI, like programs built from controlled drawings, or if they connect to systems that do. CMMC treats this kind of operational technology as a specialized asset: it has to be documented in your inventory and security plan and protected, though it isn’t held to every requirement. The usual approach is to put production equipment on its own network segment and control how files reach the machines. We help integrate equipment like CNC machines securely as part of readiness work.
What does CMMC readiness cost?
It depends on your scope, your starting point and how much of the work your team can take on. The biggest drivers are how many people and systems handle controlled data, whether you need a separate environment like GCC High, how many gaps the assessment finds, and whether you’re preparing for a self-assessment or a third-party assessment. We scope readiness as a project or compliance add-on, with every cost explained up front.
Working with Fairoaks IT
What does Fairoaks IT do for CMMC and NIST SP 800-171?
We find where controlled data lives, run a gap assessment against NIST SP 800-171, build your system security plan and plan of action, support your SPRS score, close the gaps, set up separate environments like Microsoft 365 GCC High or an isolated enclave when they make sense, provide policy and procedure templates, and keep you ready with ongoing monitoring and support during assessments.
Does Fairoaks IT certify us?
No. Level 2 certification assessments are performed by accredited third-party assessment organizations, and Level 3 assessments by the government. We get you ready for those assessments, or for your own self-assessment, and keep you ready afterward. Keeping the people who prepare you separate from the people who assess you protects you.
Have you helped other defense suppliers?
Yes. We’ve helped numerous manufacturers, large and small, that supply defense primes get ready for NIST SP 800-171 and CMMC. Our CEO, Adam Crossley, worked at Sikorsky on the Navy Seahawk program before entering IT, so we understand the contracts, the flow-downs and the shop floor.
Can you work alongside our internal IT person or current IT provider?
Yes. Readiness work can be scoped as a project on its own, alongside your internal IT team or another provider. Your IT person stays your front line while we handle the compliance-heavy pieces and the documentation, and co-managed arrangements are common.
Can you help with prime contractor flow-downs and customer security questionnaires?
Yes. We help you read the clauses in your contracts and purchase orders, figure out what level and evidence your customer actually expects, and answer questionnaires honestly with proof behind every yes. Where the honest answer is no, we help you show a plan with dates.
Where does Fairoaks IT provide CMMC readiness help?
From our offices in Franklin, MA and Belmont, NC, we support defense suppliers across Eastern Massachusetts, Rhode Island and the Charlotte, NC area, including York County, South Carolina. Much of the documentation and review work can be done remotely, and onsite visits cover network closets, plant floors and assessment days.
Manufacturing IT in Massachusetts and Rhode IslandManufacturing IT in the Charlotte, NC area
CEO
The person behind our CMMC work
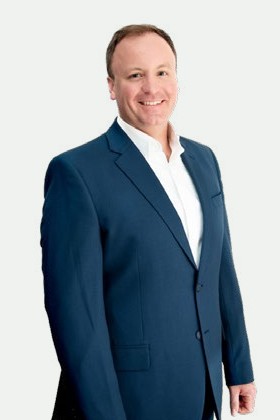
Adam Crossley is CEO of Fairoaks IT and leads our CMMC and NIST SP 800-171 work. Before IT, he worked at Sikorsky on the Navy Seahawk program and as an internal consultant and manager for United Technologies across the US, Europe and Asia, so defense contracts, flow-downs and production schedules aren’t theory to him.
Adam holds a degree in Operations Management from UMass Dartmouth, a Master of Science in Global Supply Chain from Indiana University and an MBA from UMass Amherst. He co-owns Fairoaks IT with his father, Tom Crossley, who founded the company in 1991.
Talk to us about CMMC readiness
What happens next:
- Tell us a little about your contracts and what your customers are asking for.
- We’ll reach out to set up a short conversation.
- If it makes sense for both of us, we’ll plan a readiness assessment.
Prefer the phone? Call 774-222-5500.